Who is Limenarchis for?
Limenarchis is designed for early-stage software companies that want the speed and simplicity of a PaaS while keeping production infrastructure, data, and controls in their own cloud account.
limenárchis · λιμενάρχης · lim-en-ahr-kees · Greek for "Harbor Master"
Just as a harbor master commands the port so ships can sail - Limenarchis takes the helm of your Kubernetes infrastructure so your engineers can focus on building, not managing. Production-ready, in your own AWS account, owned by you.
Overview
Limenarchis is a bring-your-own-cloud PaaS for startups. It gives teams the benefits of a managed PaaS - deployments, observability, identity, secrets delivery, Kubernetes operations, accelerated computing, and cloud operations - while running infrastructure in the customer's cloud account.
You own the cloud account, data stays with you, and Limenarchis manages the platform layer.
For teams comparing Render, Heroku, Railway, Vercel, cloud-native tools, or a self-built platform.
| Question | Limenarchis | Typical abstracted platform |
|---|---|---|
| Platform experience | PaaS workflows for CI/CD, deployments, services, observability, identity, secrets, and GPU workloads | PaaS workflows on provider-owned infrastructure |
| Infrastructure owner | Customer | Provider |
| Cloud account | Your AWS account | Provider controlled or abstracted |
| Data location | Stays in your cloud account | Often leaves your cloud boundary |
| Operations model | Managed by Limenarchis | Managed by the platform provider |
| Best fit | Early-stage companies that need PaaS speed with cloud ownership | Teams that prioritize abstraction over cloud control |
Limenarchis is designed for early-stage software companies that want the speed and simplicity of a PaaS while keeping production infrastructure, data, and controls in their own cloud account.
Consider Limenarchis when you want managed deployments, CI/CD, observability, identity, secrets delivery, Kubernetes operations, GPU workloads, and cloud operations without giving up ownership of the underlying cloud environment or when data ownership is important to you.
Limenarchis may not be appropriate for teams that do not want customer-owned cloud infrastructure, do not have data retention concerns, or companies that already have a mature internal platform engineering organization.
Limenarchis manages the platform layer: infrastructure provisioning/scaling, Kubernetes operations, CI/CD pipelines, application deployments, GPU workloads, model hosting, observability, tracing, logging, alerting, identity, secrets delivery, networking, DNS, security controls, and ongoing maintenance.
AWS today. Every resource Limenarchis provisions - networks, clusters, load balancers, DNS, certificates, and CI/CD - lives in your own AWS account.
No. Limenarchis CI/CD builds, scans, and deploys inside your AWS account, and images, logs, and run history stay there.
Features
Kubernetes means "helmsman." Docker means "dockworker." Limenarchis means "harbor master." We're the next chapter in cloud's nautical story - commanding your entire fleet with full visibility.
Production-ready clusters in your AWS account, with autoscaling, one-click upgrades, monitoring, and maintenance handled for you.
Learn morePush to build, scan, and deploy - inside your own AWS account. Registries, deploy roles, and cluster access are configured for you.
Learn moreEnd-to-end encryption with SSL at ingress and mTLS inside your network. JWT authentication at the edge.
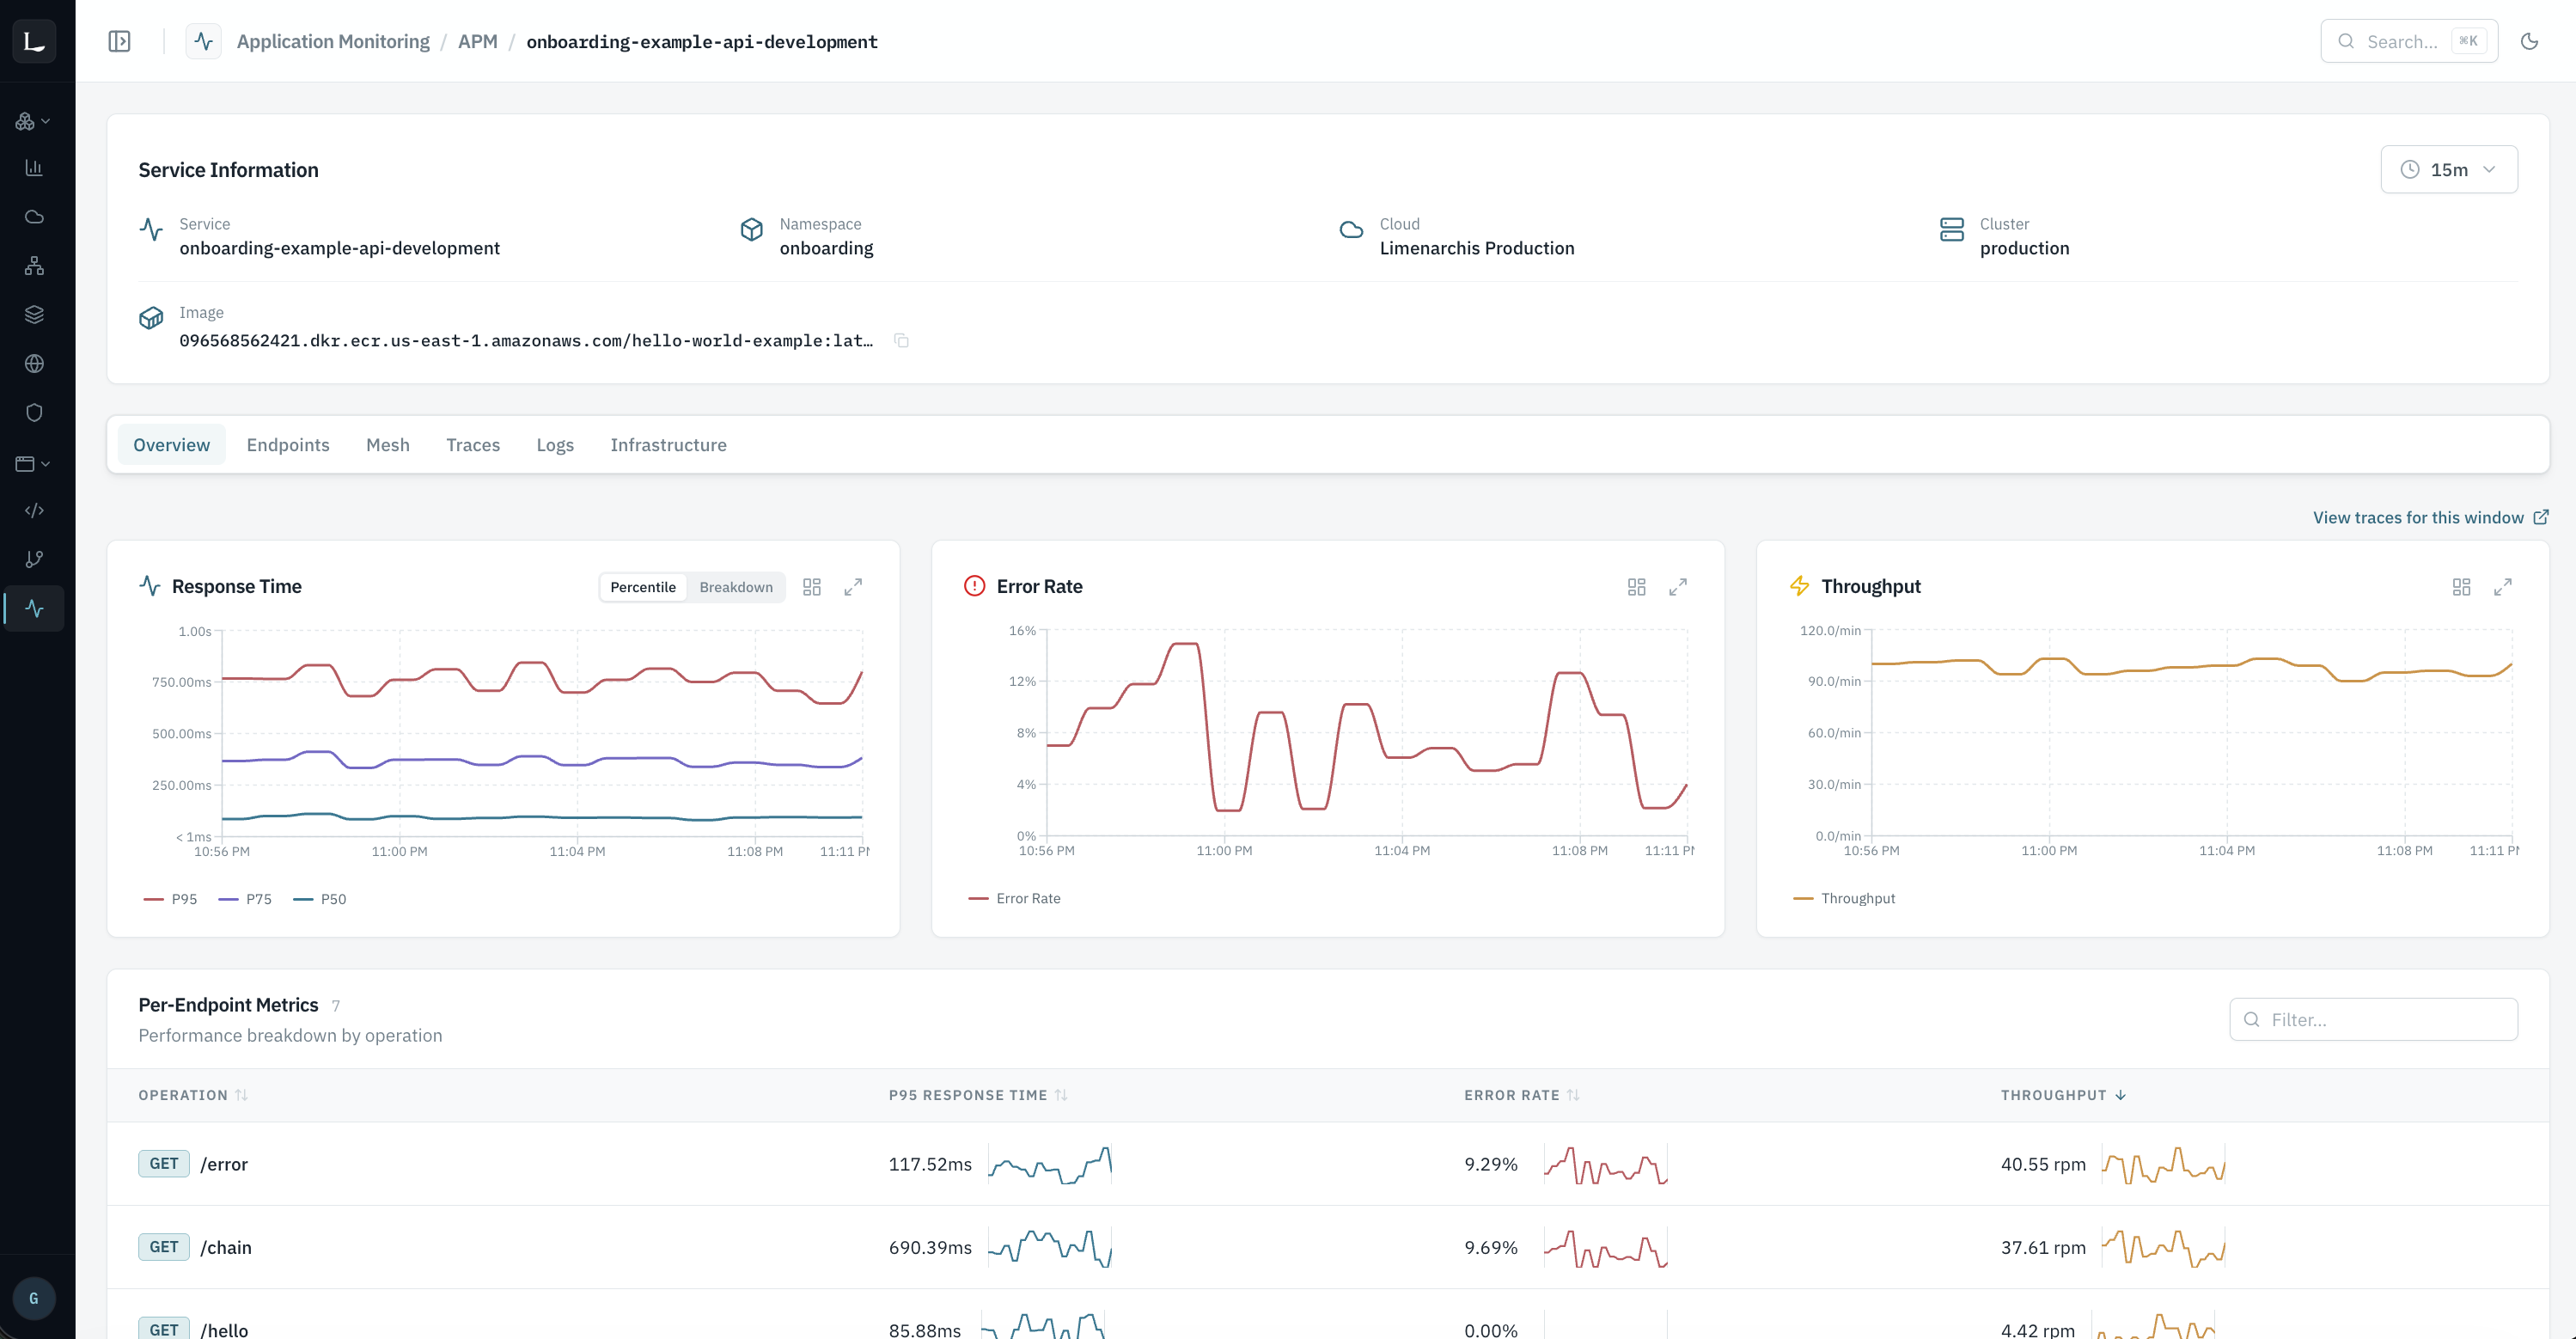
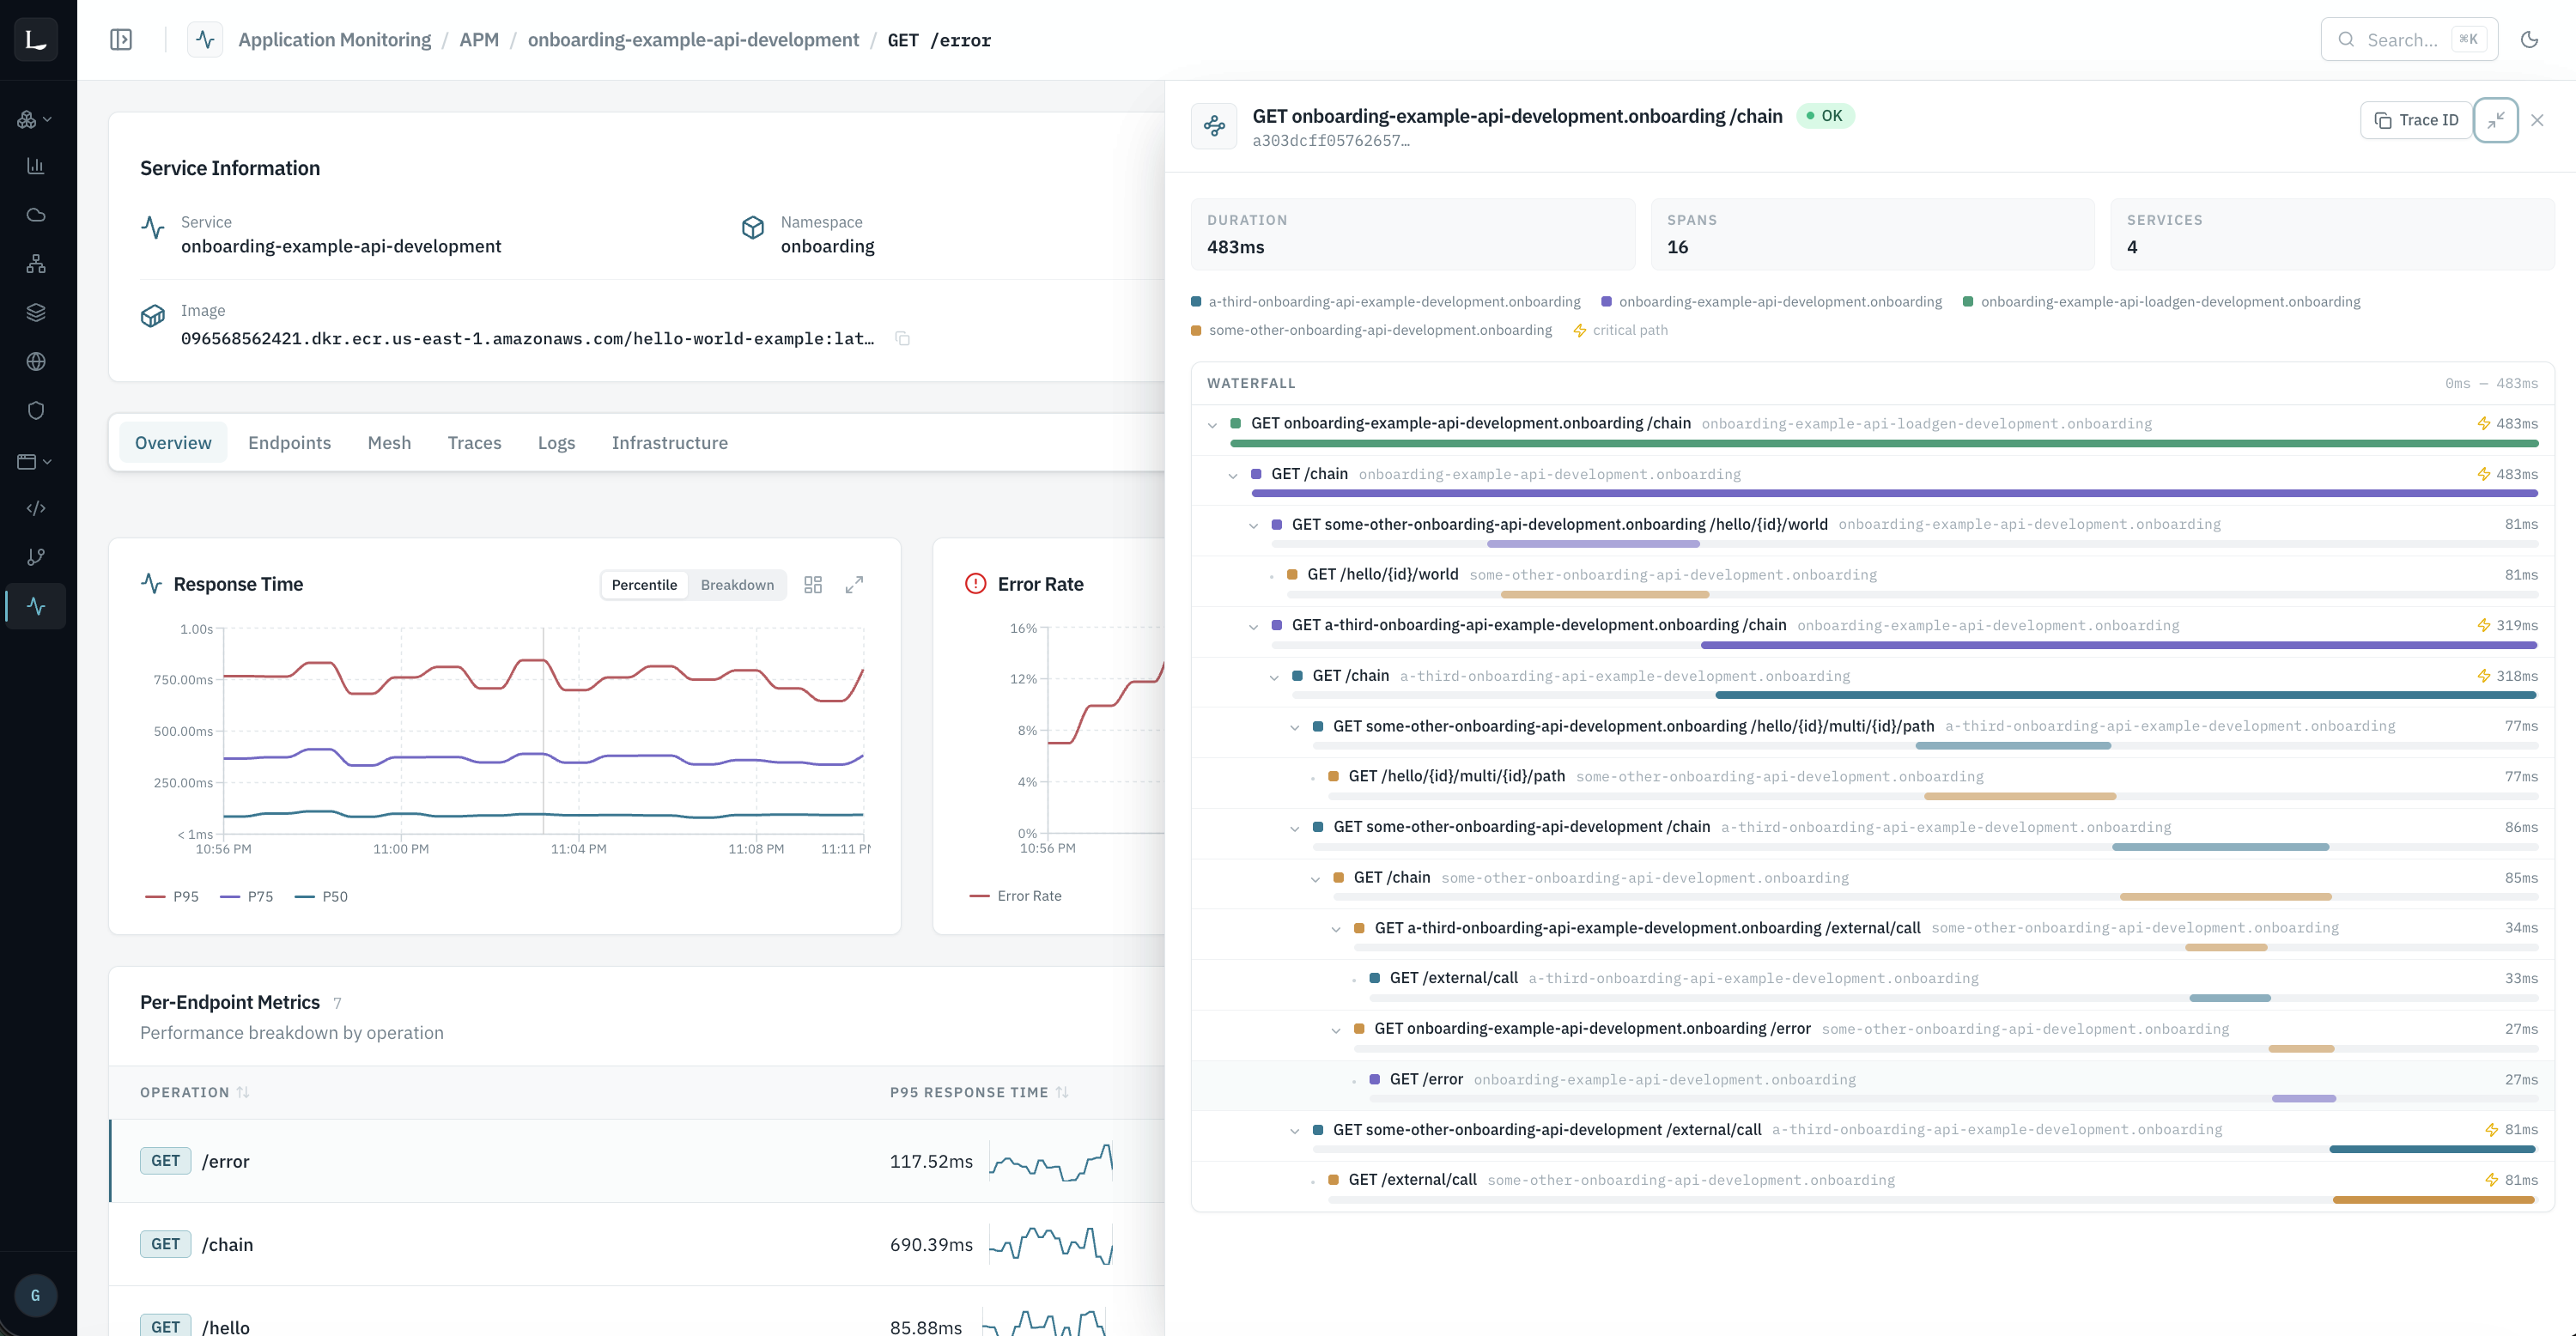
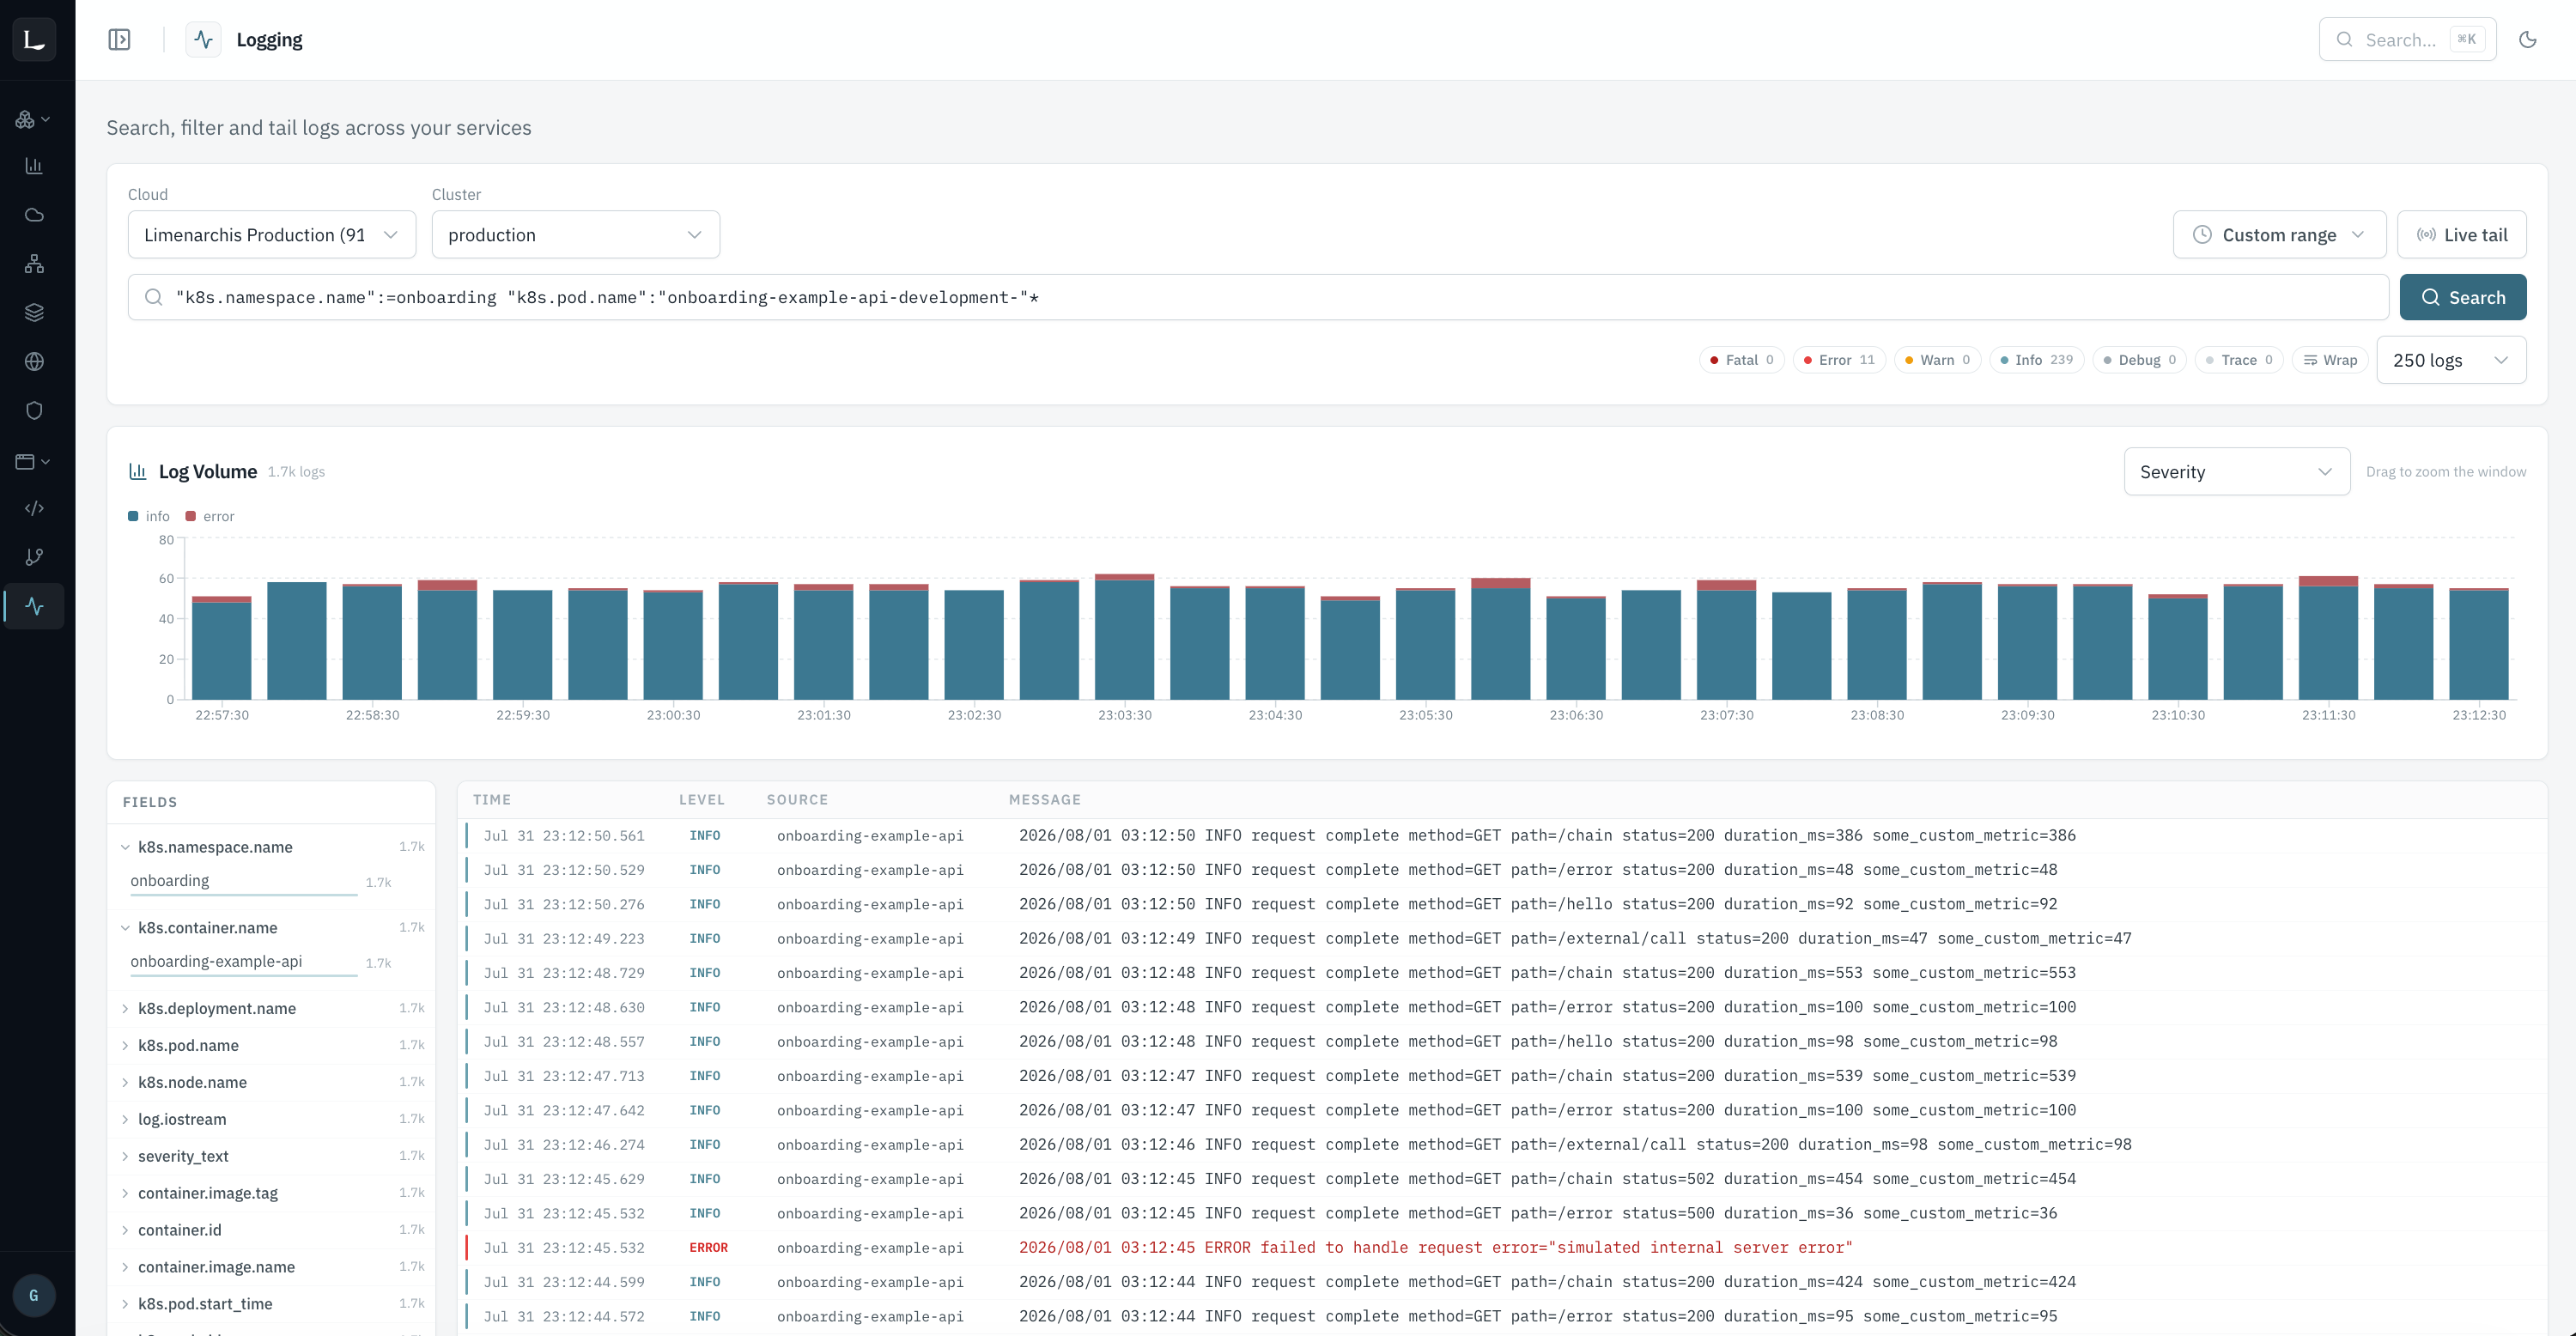
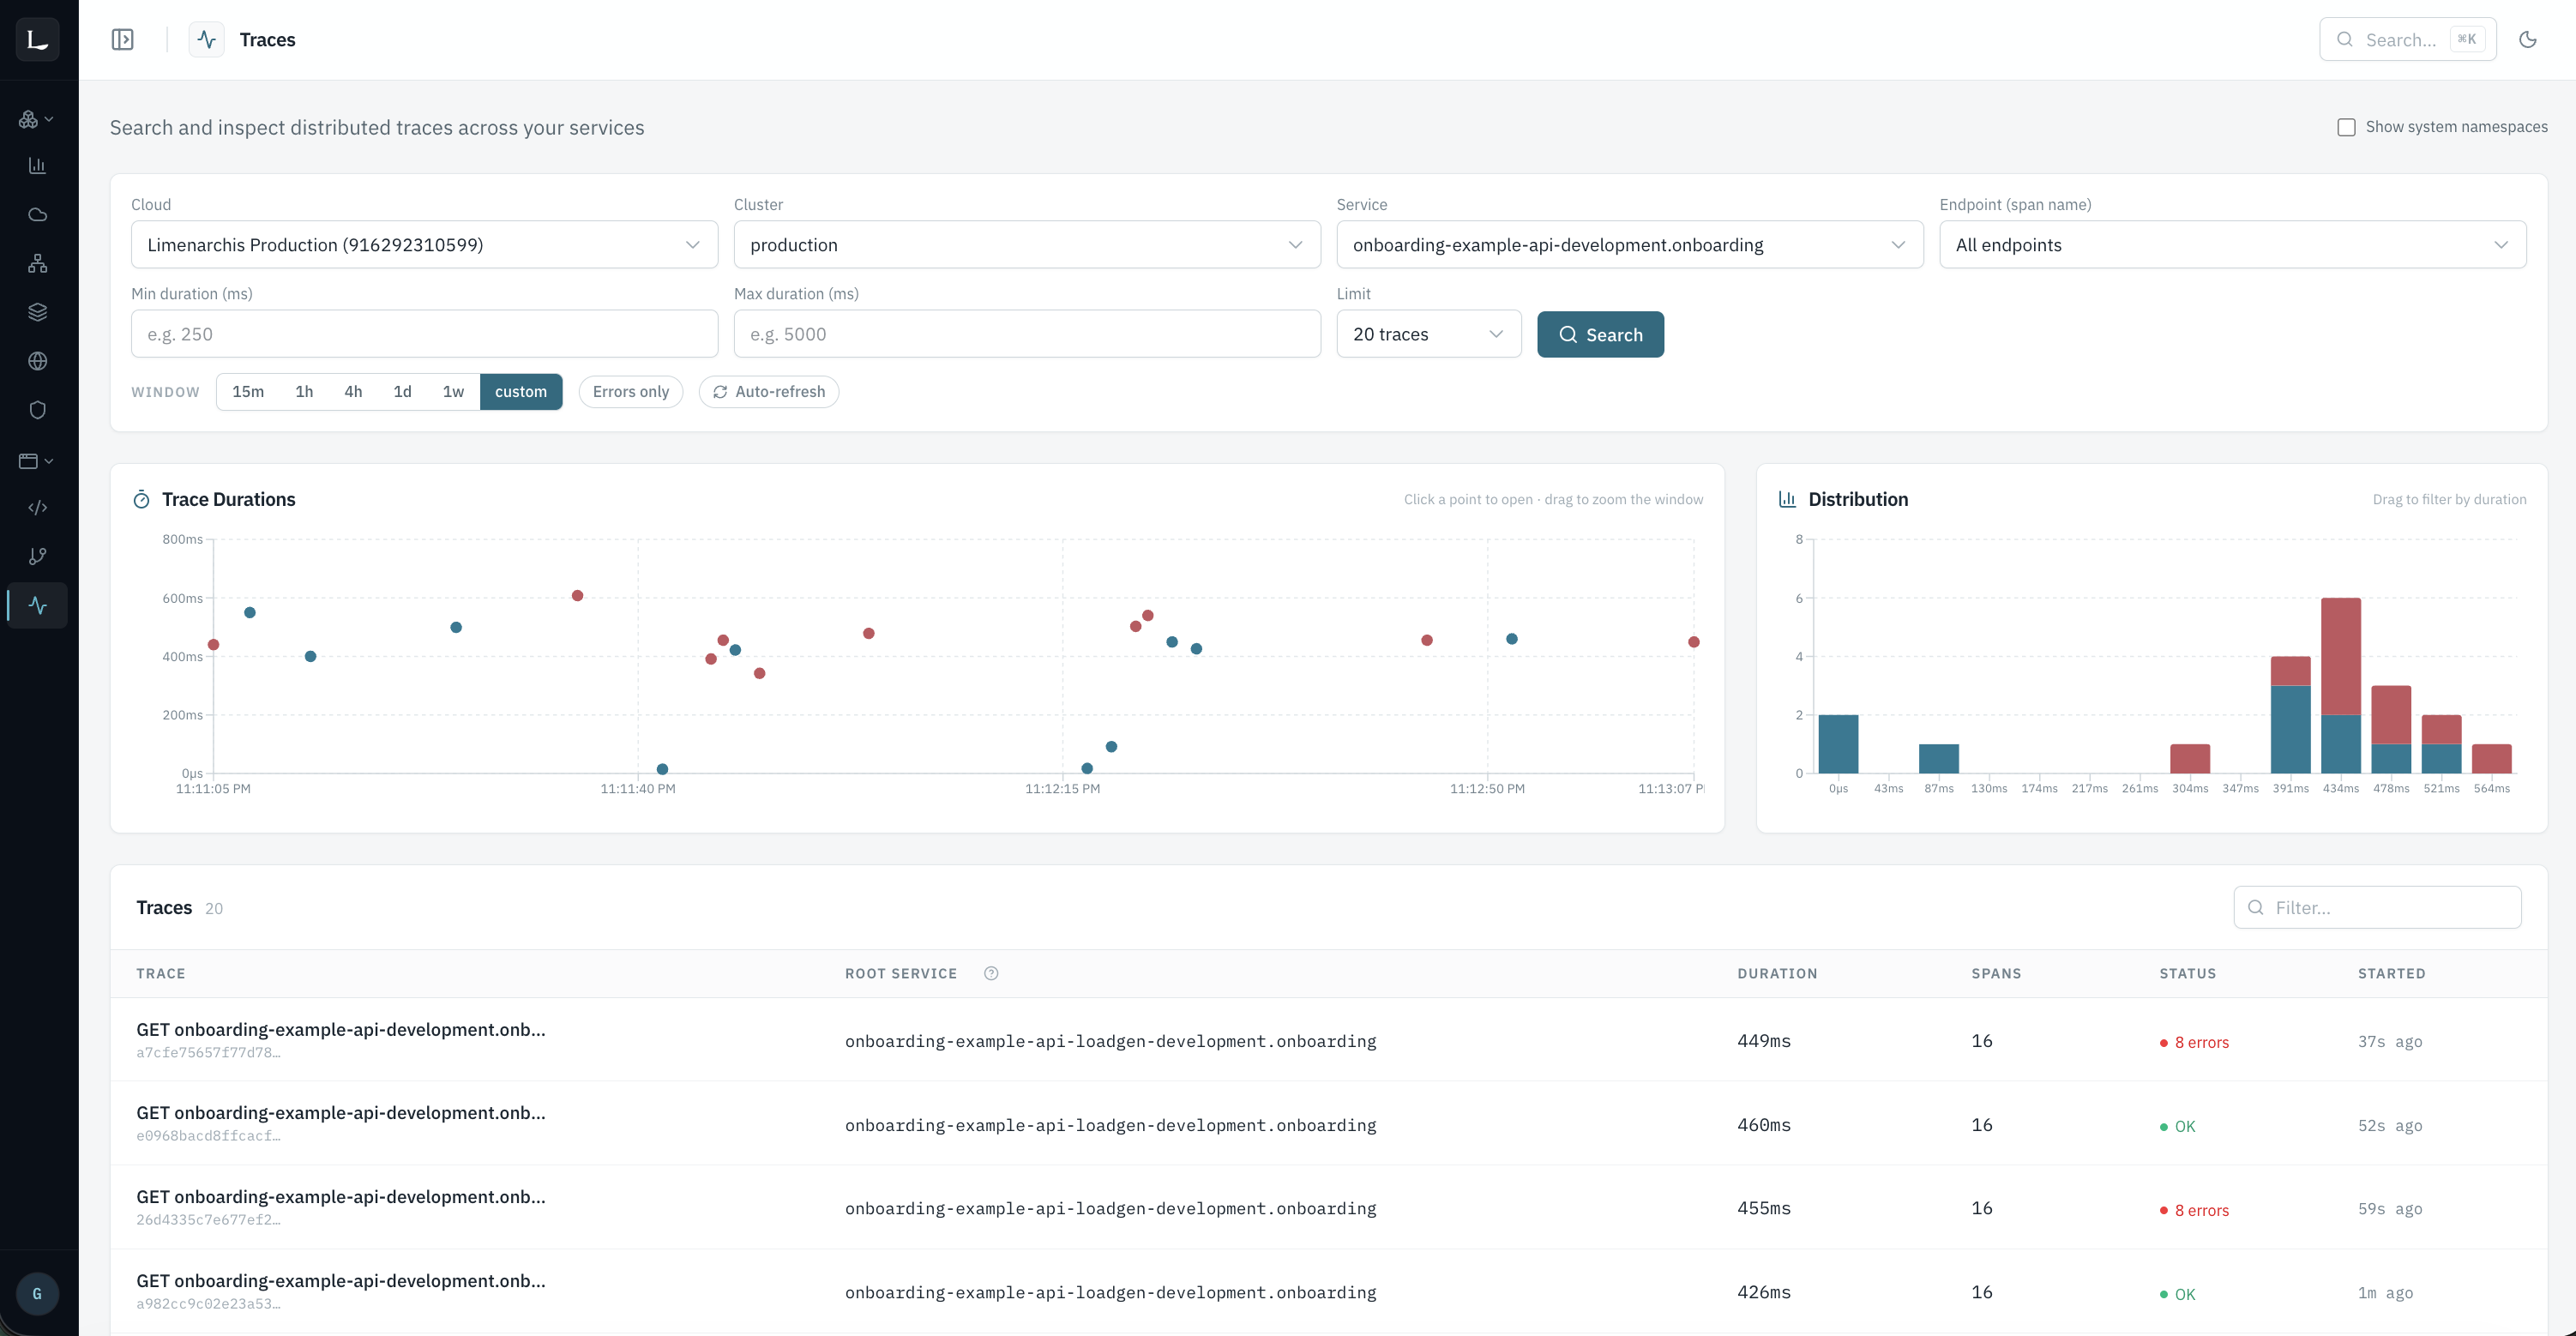
Learn moreBuilt-in APM, tracing, logging, alerting, and dashboards. Deploy with Limenarchis and every service is auto-instrumented - no code changes required.
Learn moreRun GPU workloads for custom models, LLMs, open-weight models, and training jobs with GPU-specific observability.
Learn moreSeed open-weight LLMs for hosting, run any open-weight model, and scale GPU capacity from zero when idle.
Learn moreLoad balancing, ingress controllers, and DNS management. Everything configured and ready to go.
Learn moreOptional identity provider with JWT authentication at the network edge. Unauthenticated traffic never reaches your services.
Learn moreAccess to infrastructure and SRE expertise without the full-time hire. We are here when you need us.
Managed Infrastructure
Networks, clusters, load balancers, DNS, certificates, and identity - each a form in the console, provisioned in your own AWS account and maintained by Limenarchis. The guided setup takes about 20 minutes.
EKS with service mesh, ingress, autoscaling, and telemetry installed. One-click upgrades, one version at a time.
Multi-AZ VPCs with public and private subnets, NAT gateways, and default-deny security groups.
Load balancers that terminate TLS with certificates that validate and renew themselves, then mutual TLS inside the cluster.
A Route 53 zone per domain, with records written for you as resources are created.
Optional signup, login, and JWT enforcement at the cluster edge, so unauthenticated traffic never reaches your services.
Every action runs through an IAM role you create, on temporary credentials. No long-lived keys.
Observability
Deploy with Limenarchis and every service is instrumented automatically. The data is stored on your clusters, in your account, and there are no per-user licenses or ingestion bills.
Latency, error rate, and throughput for every service and endpoint.
Follow one request across services, and see every service-to-service call.
Every container log, searchable, tailable, and turnable into metrics.
Alerts evaluated on your own cluster, sent to Slack, email, or webhooks.
Save the charts your team relies on and share them across the organization.
Query metrics, traces, and logs with the same syntax, on one screen.
CI/CD
Most CI/CD hands you a runner and leaves the hard part to you: registries, IAM roles, Kubernetes RBAC, service accounts, and secrets. Limenarchis CI/CD is already connected to your clusters and clouds - secure, least-privilege, and running entirely in your AWS account.
What you configure
Stages that test, build, scan, and deploy - committed to your repository.
Bind the pipeline to environments like staging or production, with optional approvals and branch rules.
Grant secrets from your own Secrets Manager by alias.
That's it. Commit the file and the next push runs it.
What Limenarchis sets up for you
ECR in your CI/CD account and in each target account, ready to push to.
Separate, scoped publish and deploy roles created for every target - no ARNs or trust policies to write.
Kubernetes access limited to the namespaces a target allows. Namespaces are created on first deploy.
Values go from Secrets Manager straight to the build. Never copied, never in run history.
A dedicated node pool in your cluster that scales to zero when nothing is running.
Pipeline files cannot widen their own access, and forked pull requests get no secrets or targets.
Accelerated Computing
Limenarchis treats GPUs as first-class cluster resources for model training, LLM inference, custom models, and open-weight model hosting inside your AWS account.
Accelerator health plus model-serving metrics - latency, queue depth, tokens, and cost per model - in the same observability suite as everything else.
Seed open-weight LLMs for hosting or run any open-weight model your team needs to serve.
Scale GPU capacity down when idle and back up when workloads need accelerated compute.
Why Us
Most startups face an impossible choice when it comes to infrastructure. All three options burn runway:
Pull devs off building features to cobble together infrastructure. Get subpar solutions that need rebuilding later.
Deploy on Heroku/Vercel. Costs explode at scale. Migration becomes a nightmare when you outgrow them.
Hire contractors to build it. Pay premium rates, still no expertise in-house, and they leave with all the knowledge.
Production infrastructure in YOUR cloud. You own it, your data stays with you, zero vendor lock-in. We bring the expertise and automation. Scale from day one to millions of users on the same platform.
Demo
See how simple it is to deploy a complete production infrastructure. Bring your cloud account and domain, fill out a few forms, and your fleet is live.
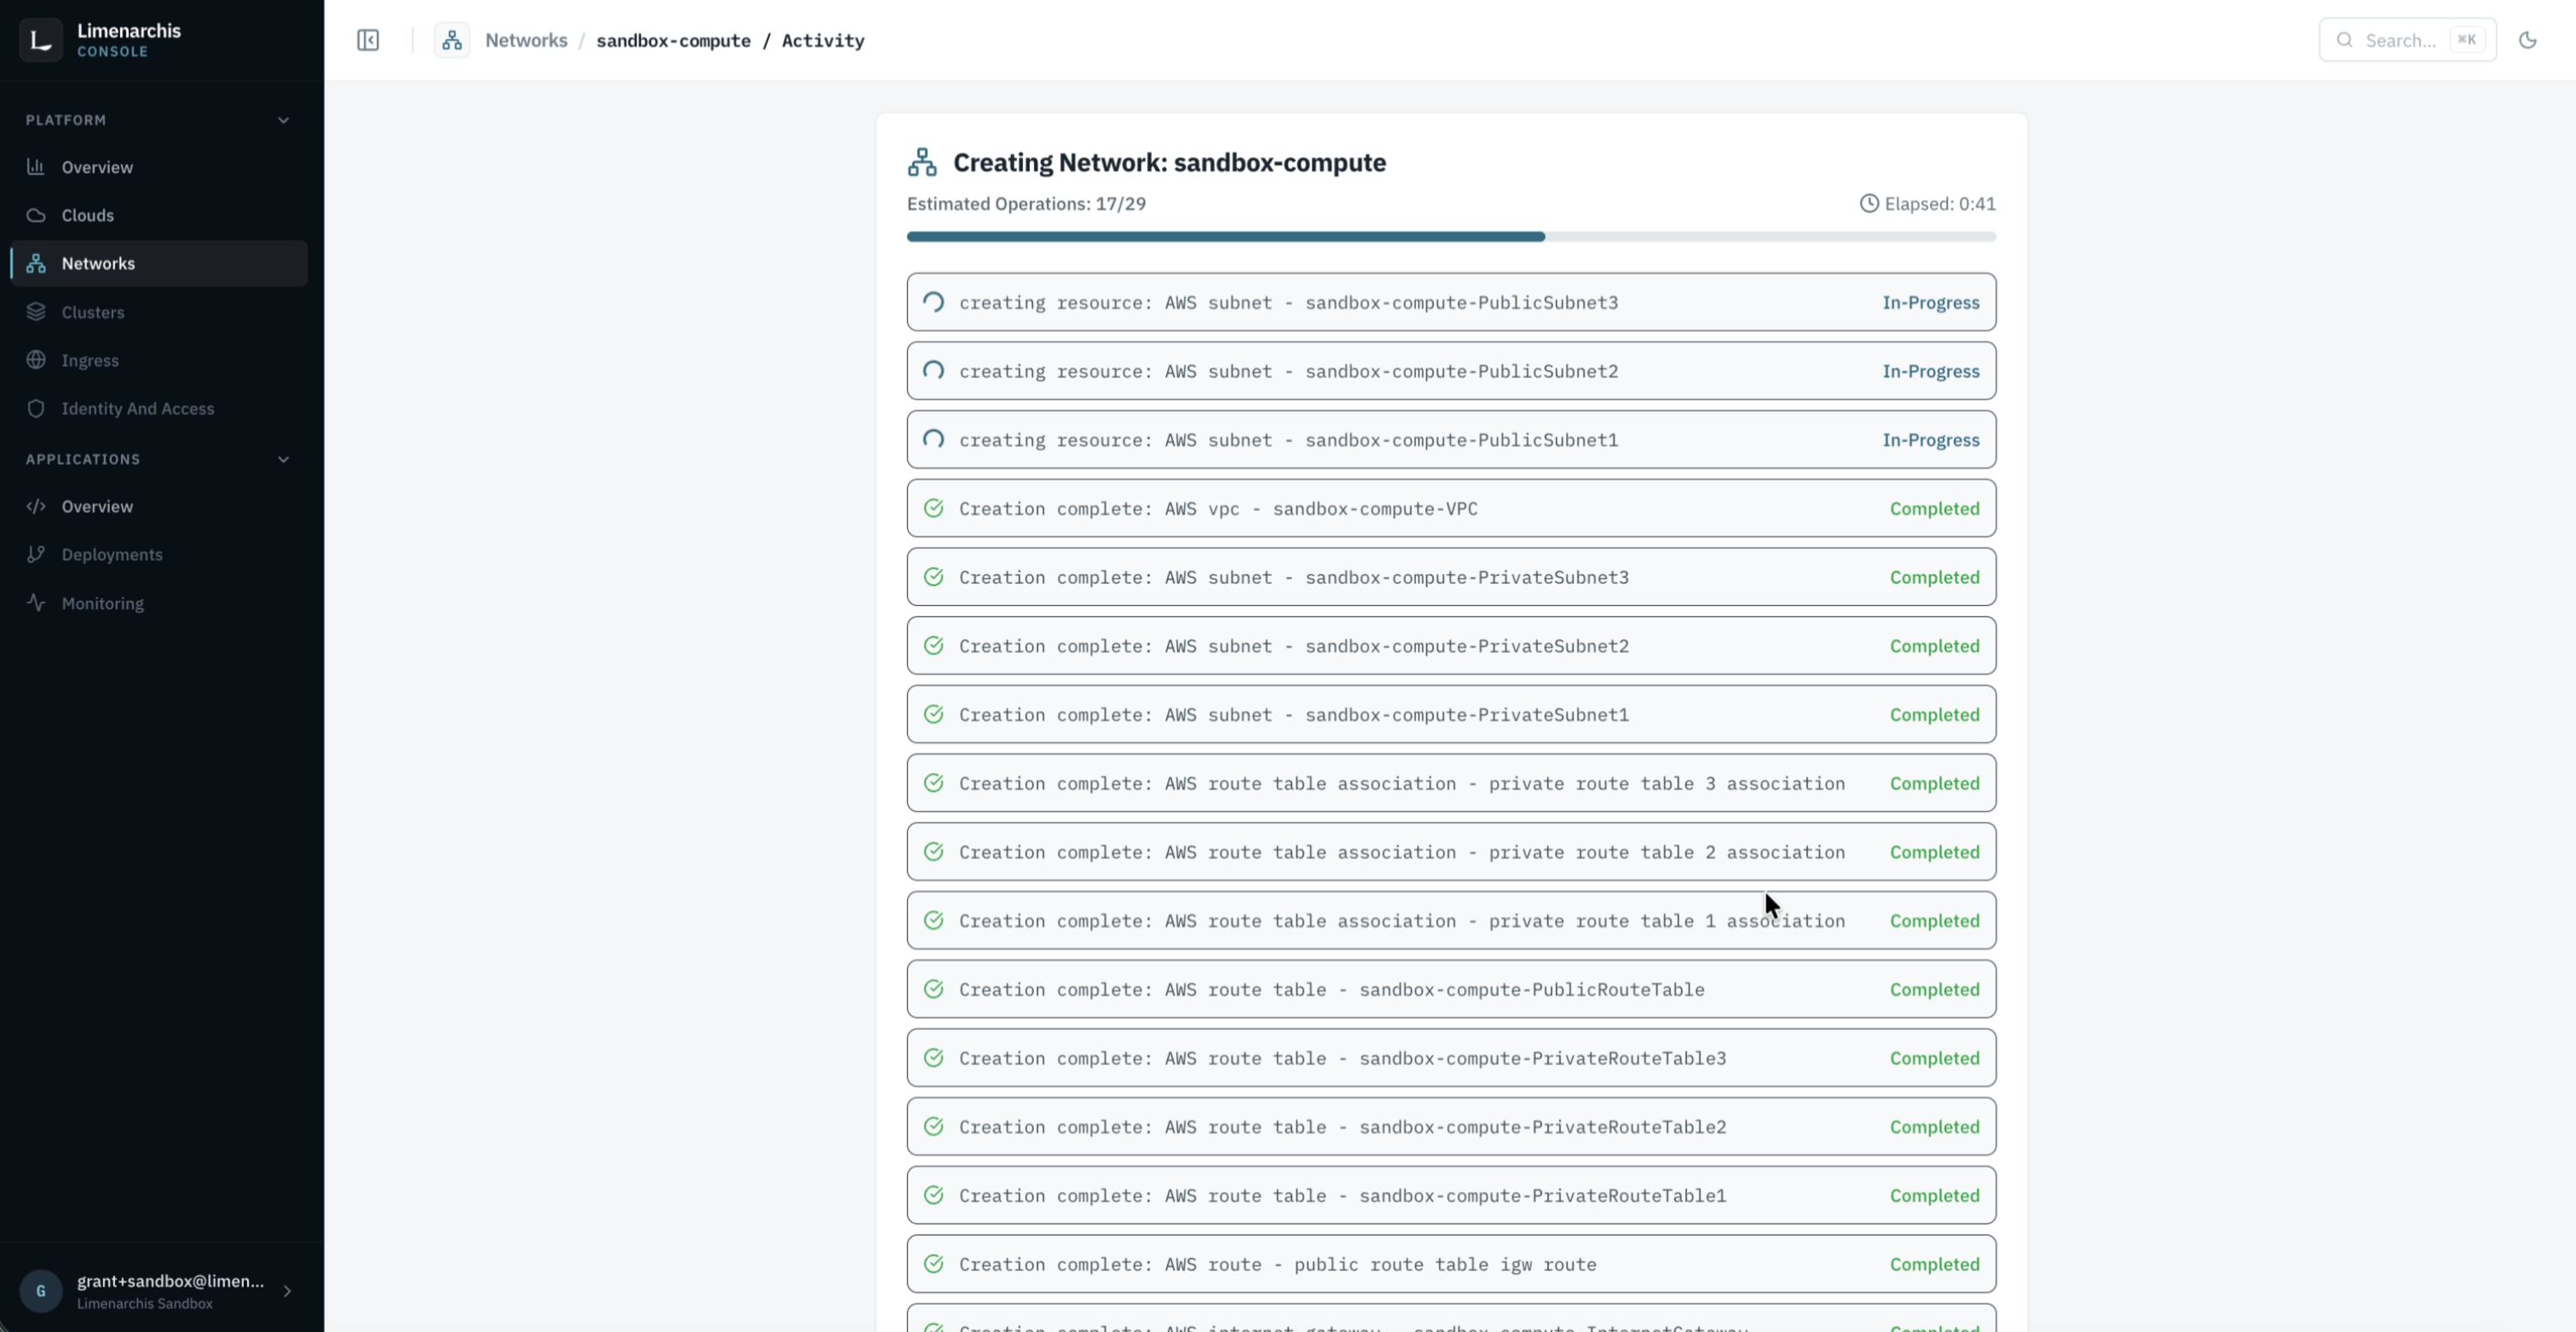
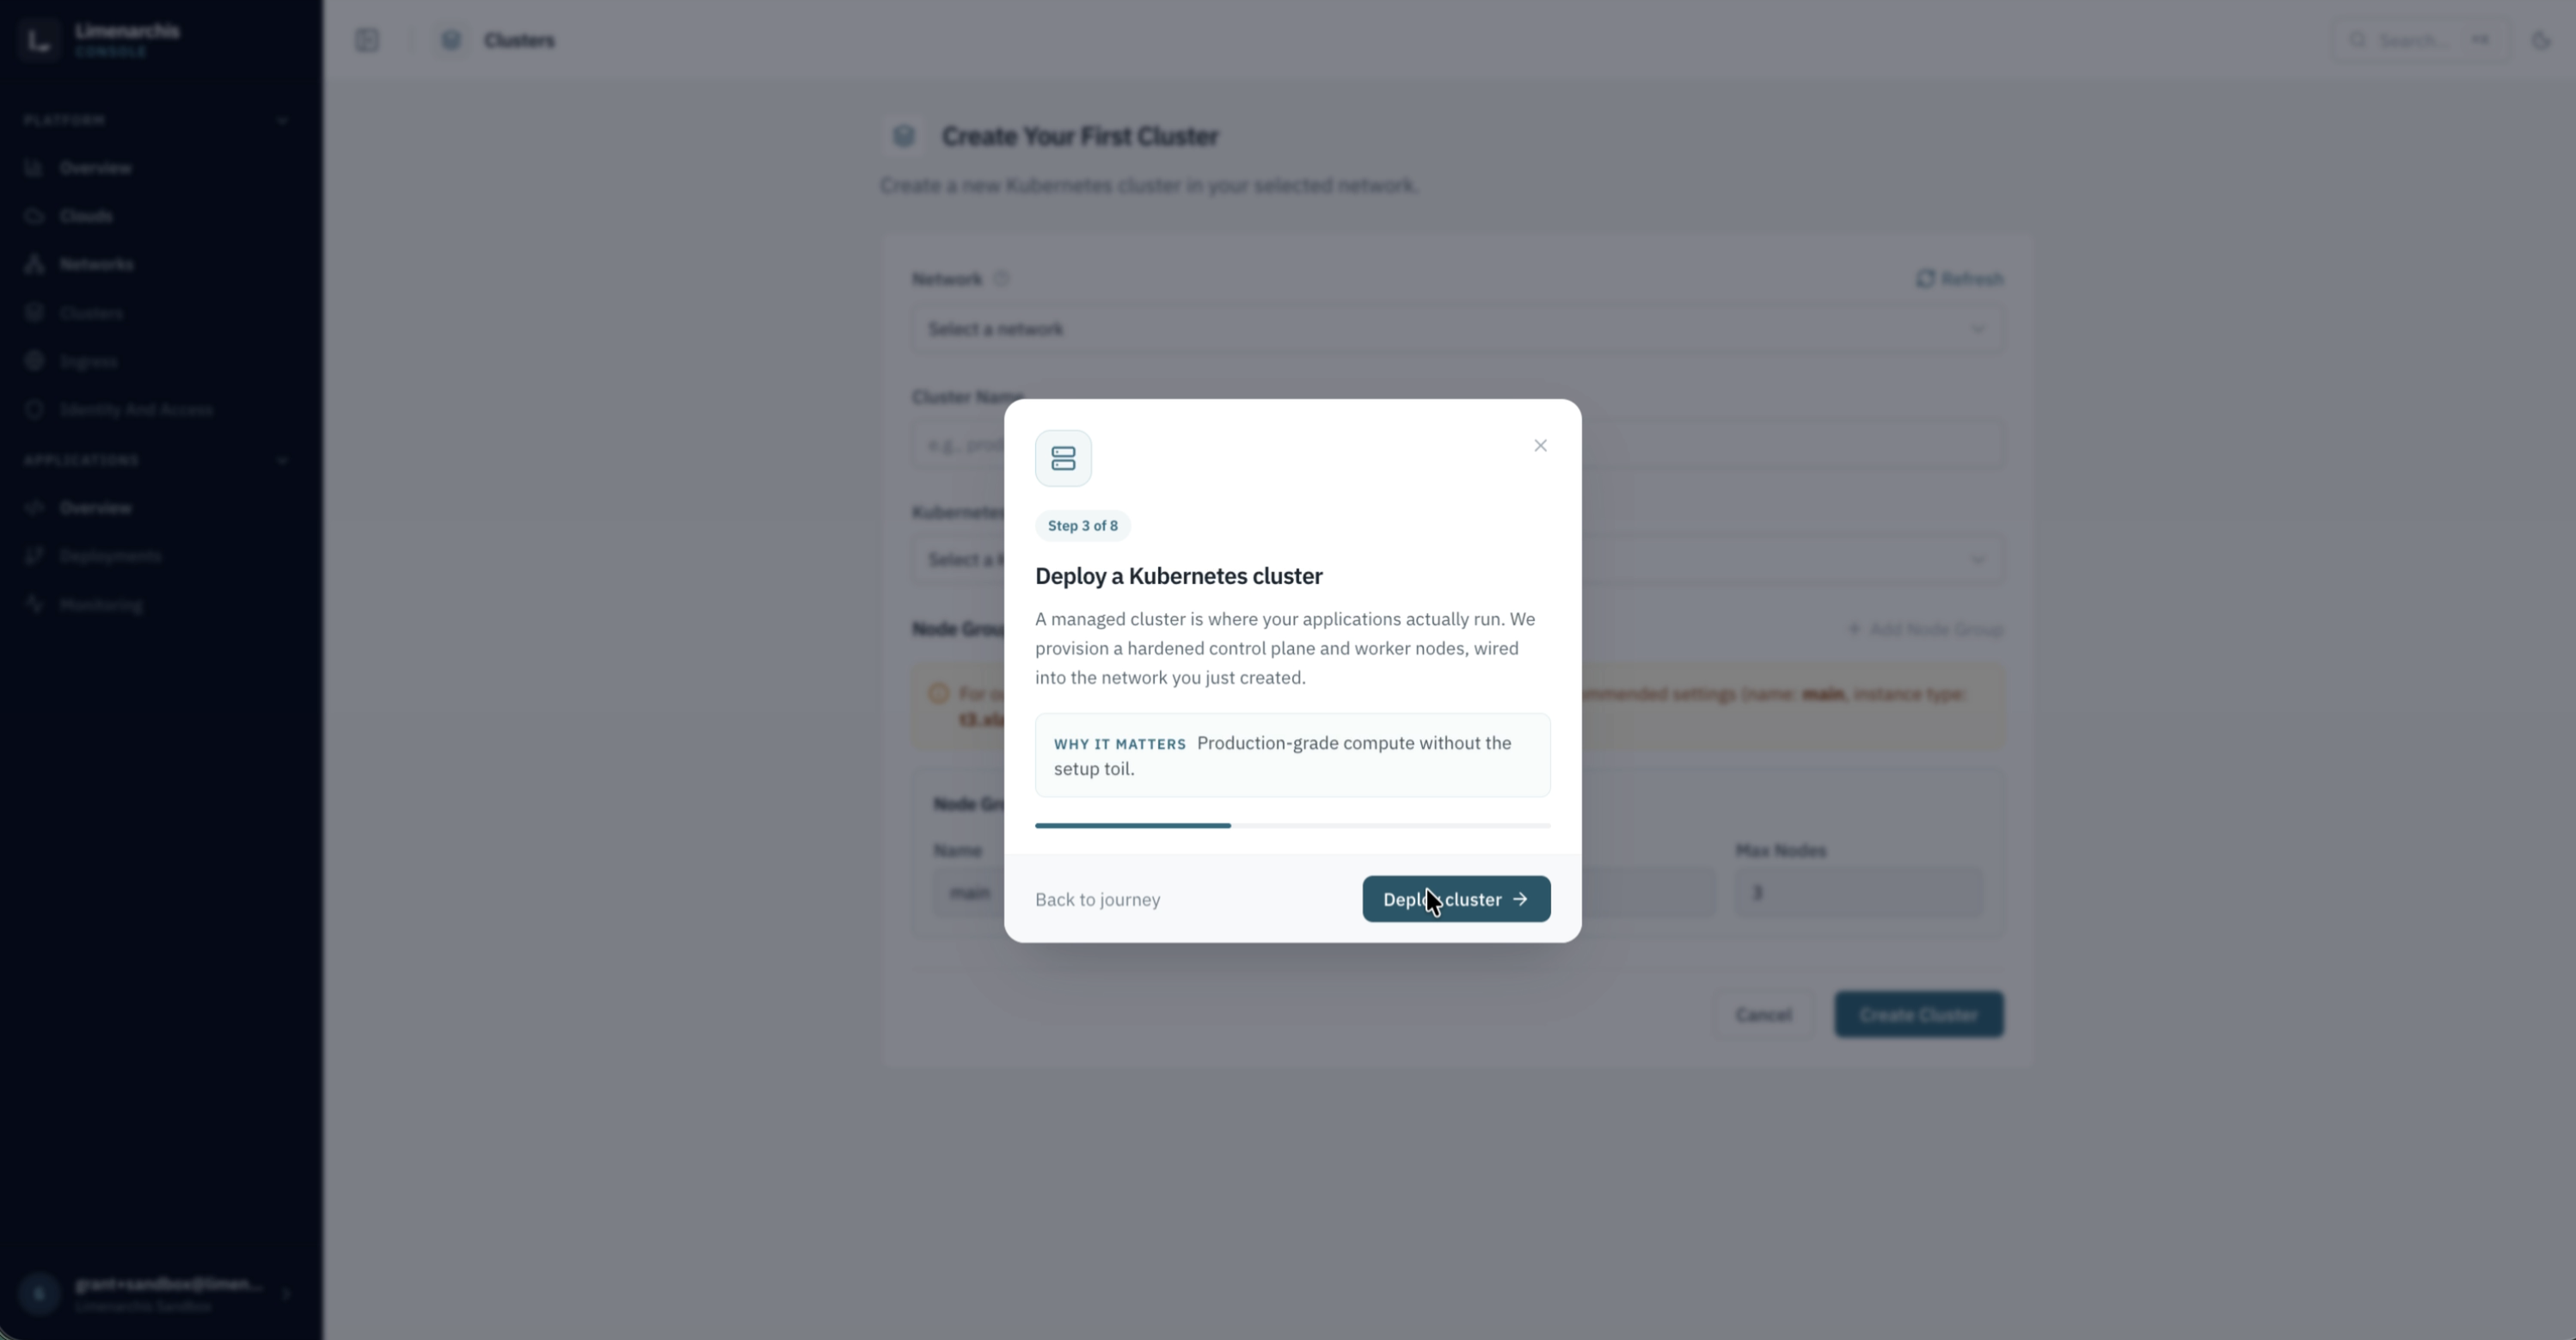
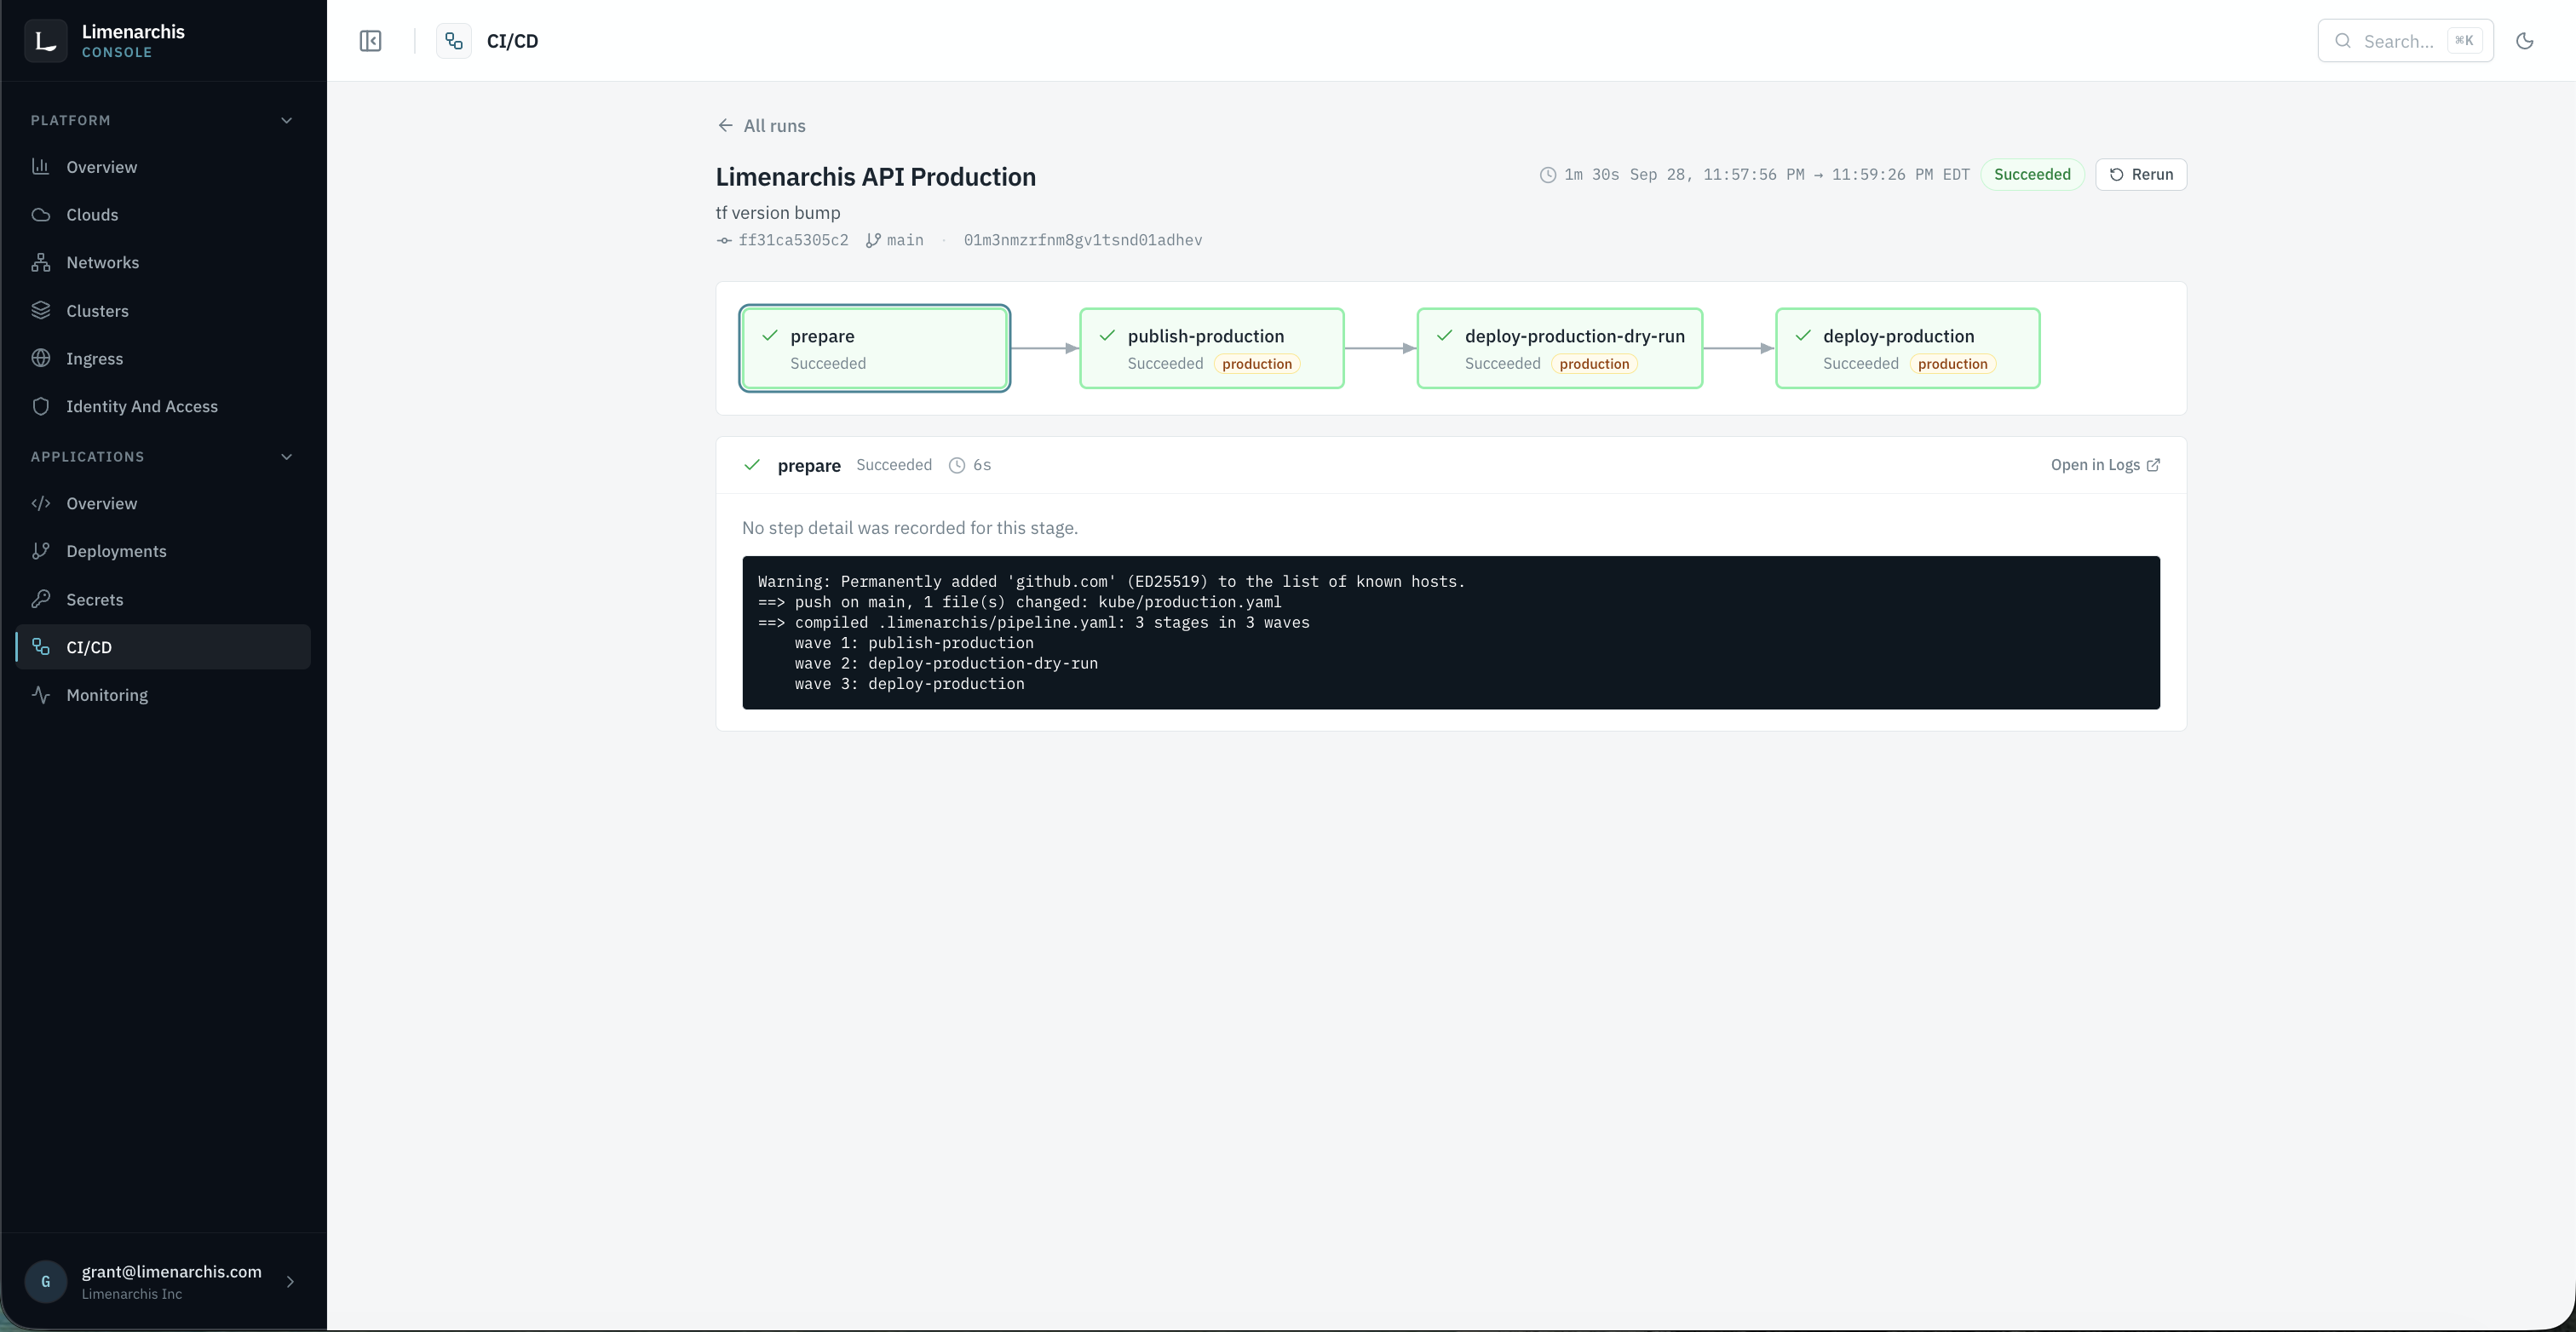
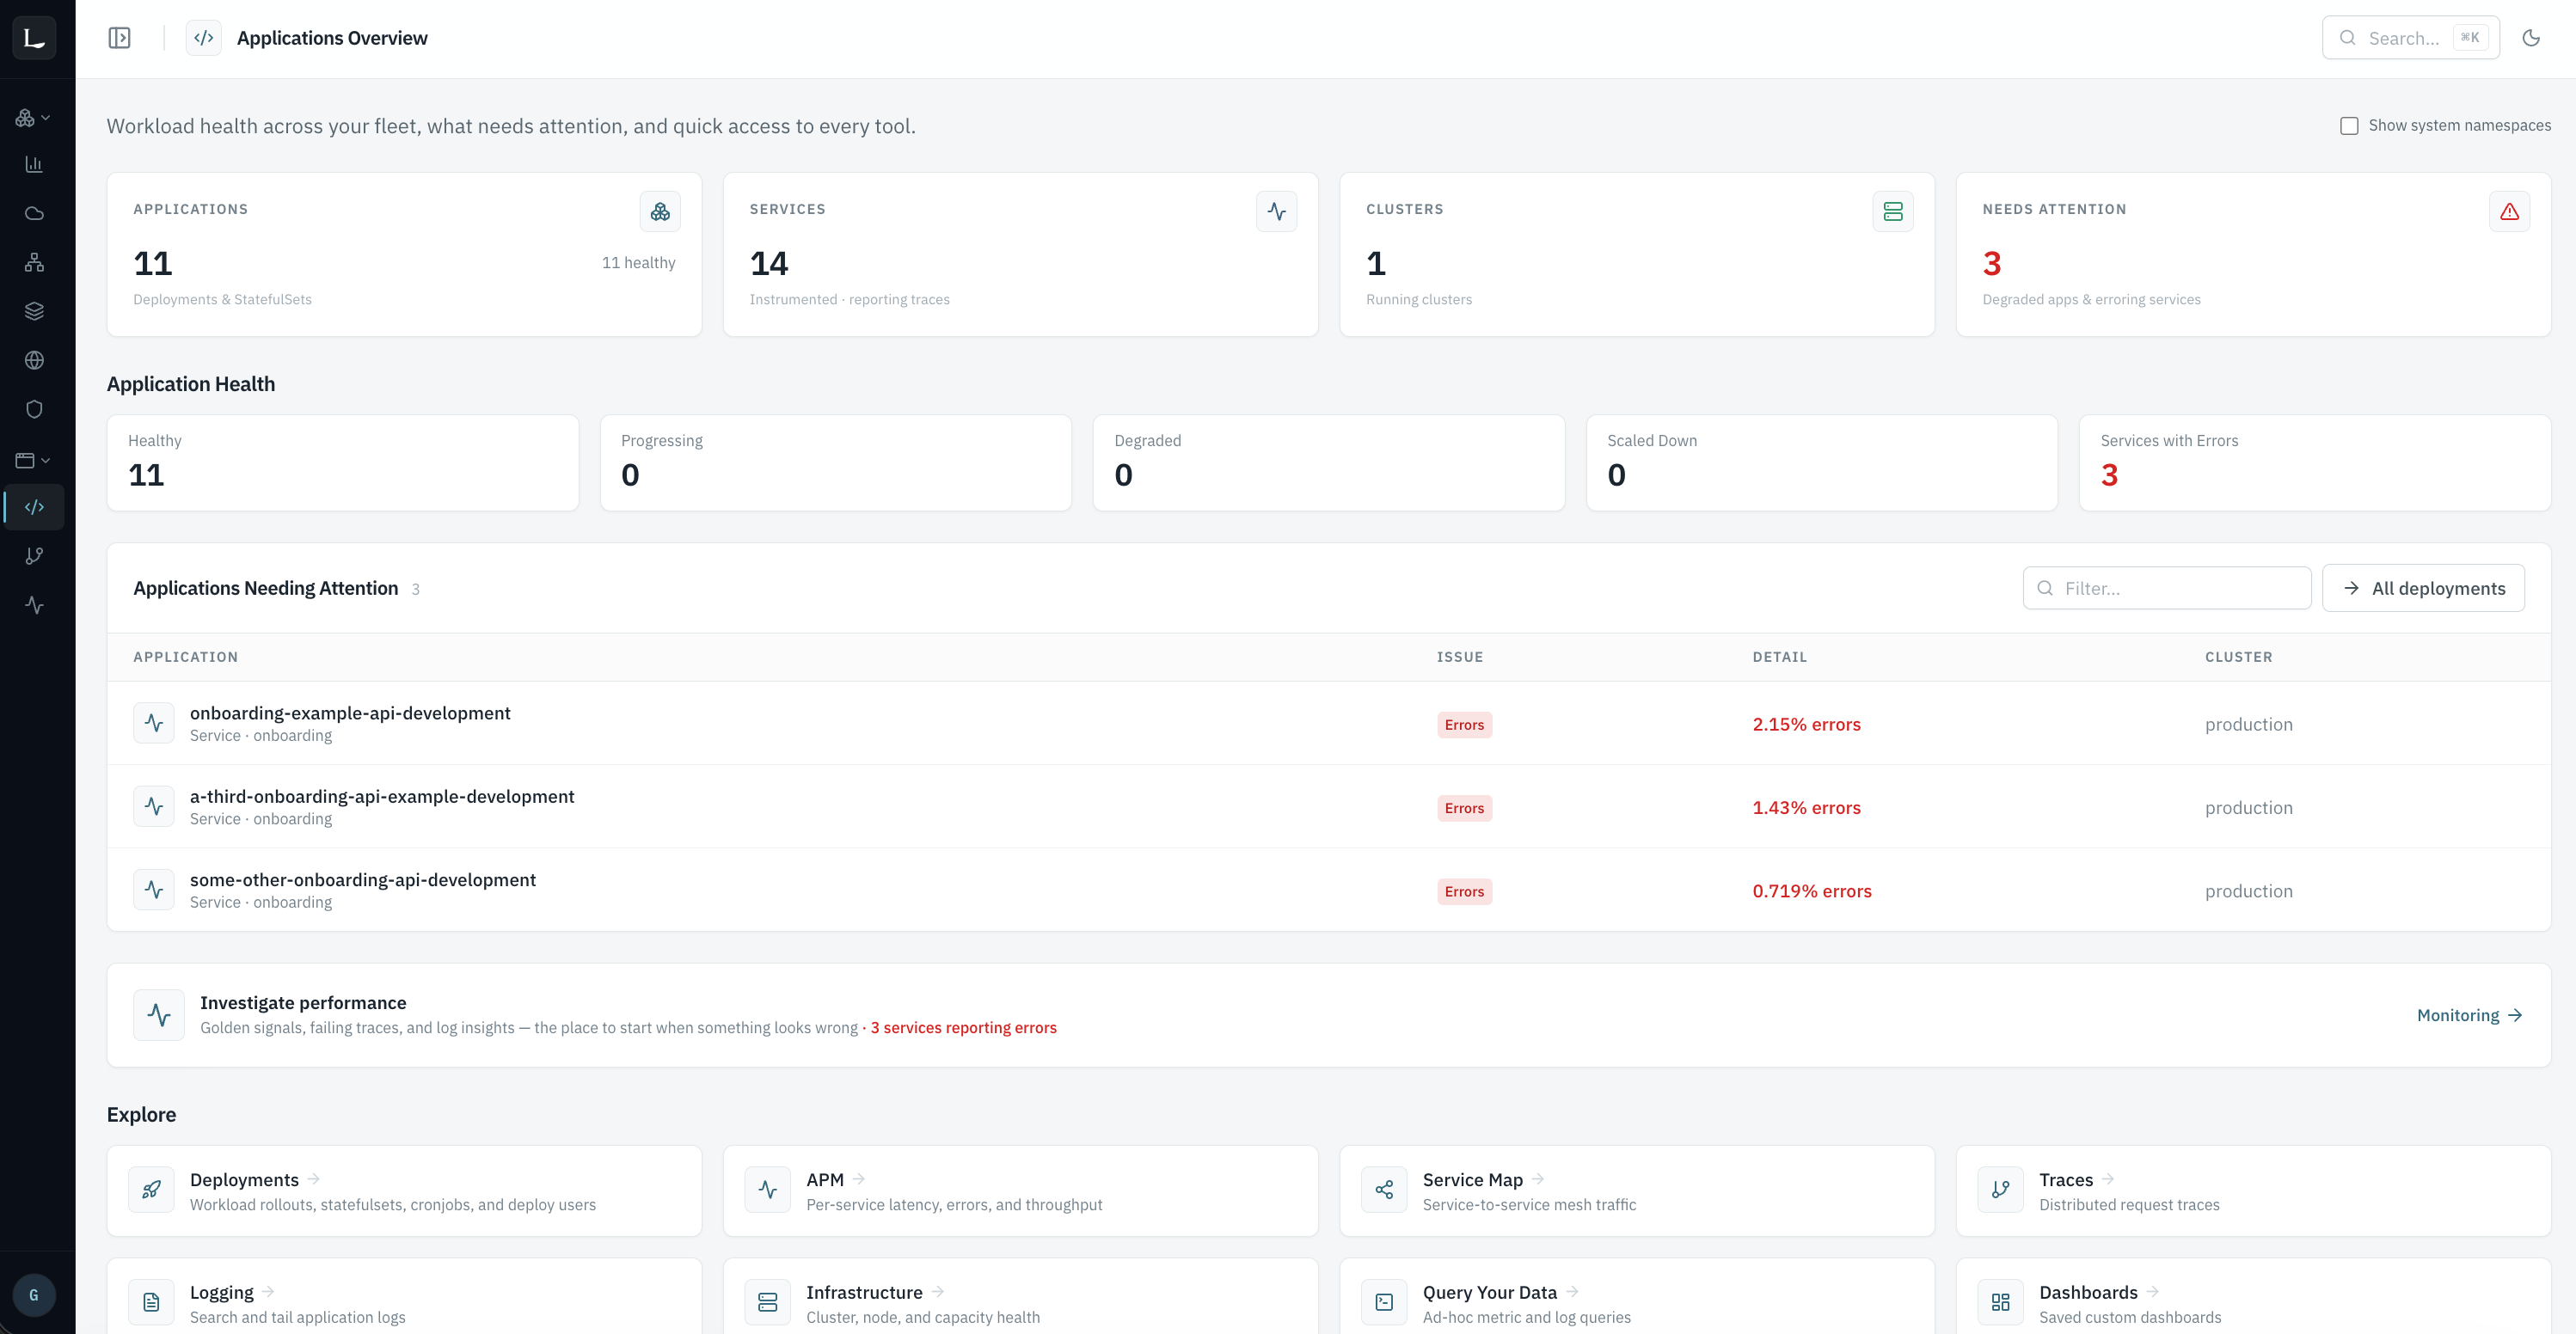
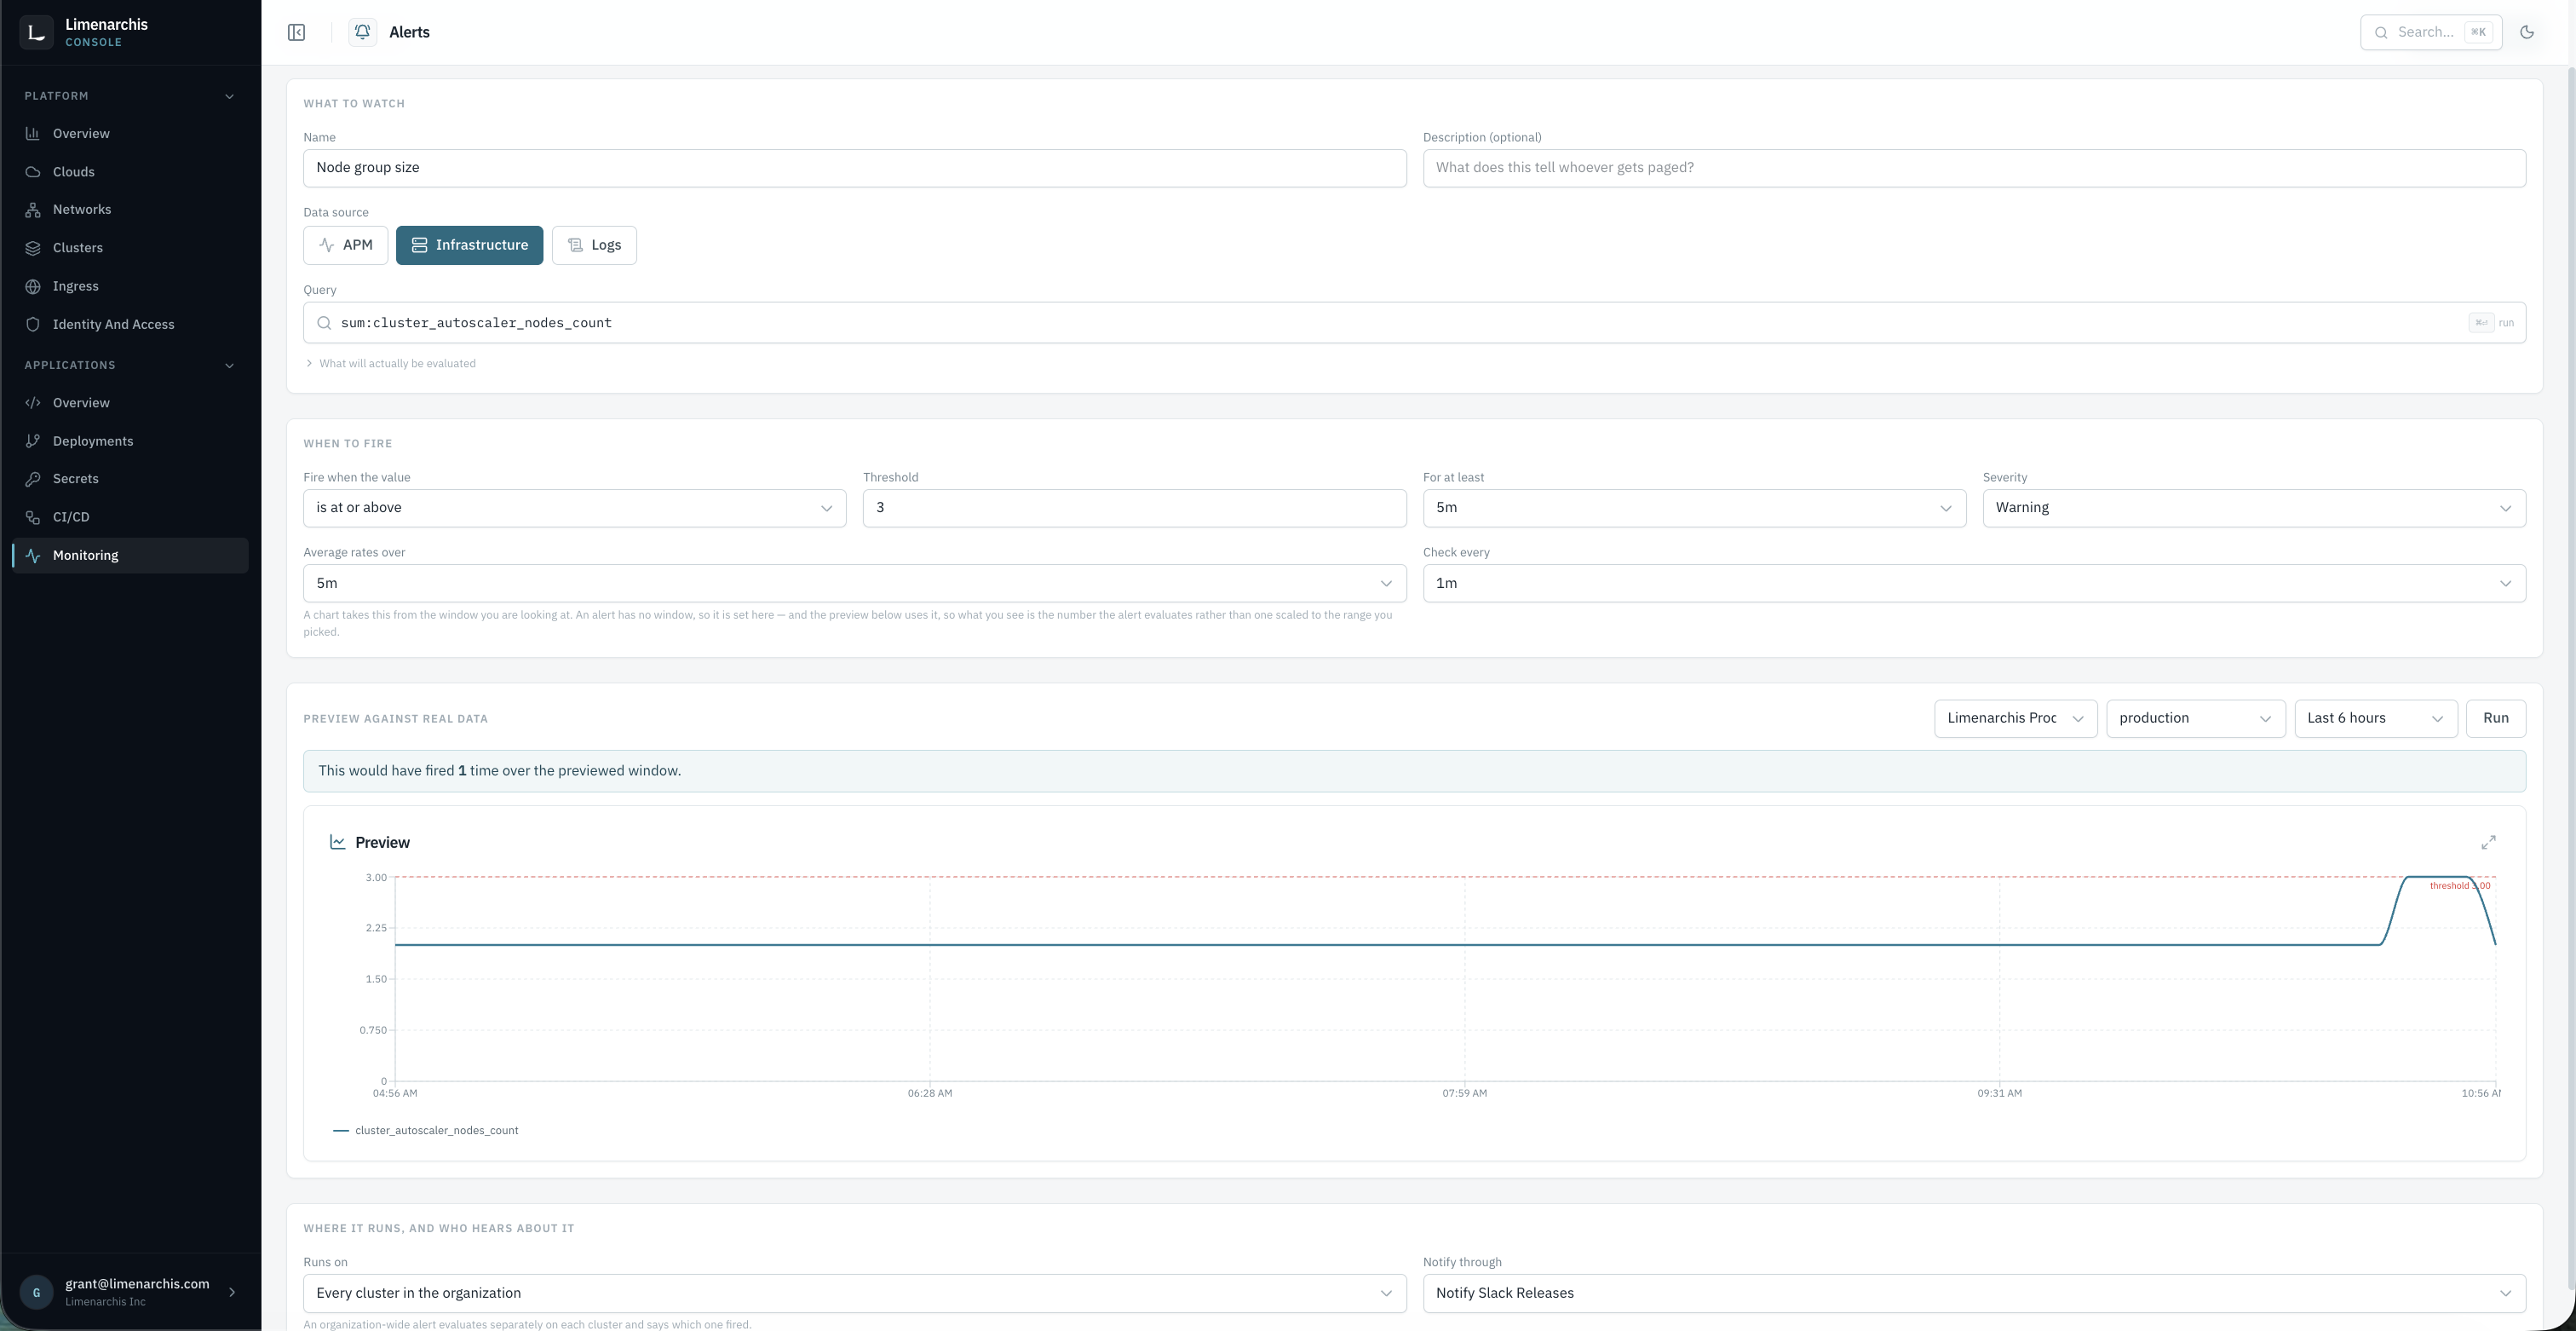
Spin up a hardened VPC with public and private subnets in a few clicks.
Pricing
Simple, transparent pricing based on your actual infrastructure costs. No hidden fees, no surprises.
We charge 25% of the AWS infrastructure Limenarchis manages: compute, storage, the Kubernetes control plane, load balancers, NAT gateways, DNS, and encryption keys. The Billing page in the console shows that spend by cloud and by resource type, next to your projected fee.
You get enterprise-grade platform management for a fraction of the cost of hiring SREs.
You get an infrastructure that scales with you, not vendor lock-in with exploding future costs.
You get built-in native observability. No need to burn runway on an expensive monitoring platform with hard to manage costs.
Perfect for startups and growing companies
of the AWS infrastructure we manage
For organizations with specific requirements
tailored pricing
Team of 5 developers + 1 SRE, $1,000/mo of managed AWS infrastructure
Pay-as-you-go pricing, full platform users
Per-user price from New Relic's published usage plan. Both columns exclude the AWS infrastructure itself, which you pay AWS directly either way.
Currently in closed beta. Join the waitlist to get early access.